A Serious Security Threat to PHP-Based Websites
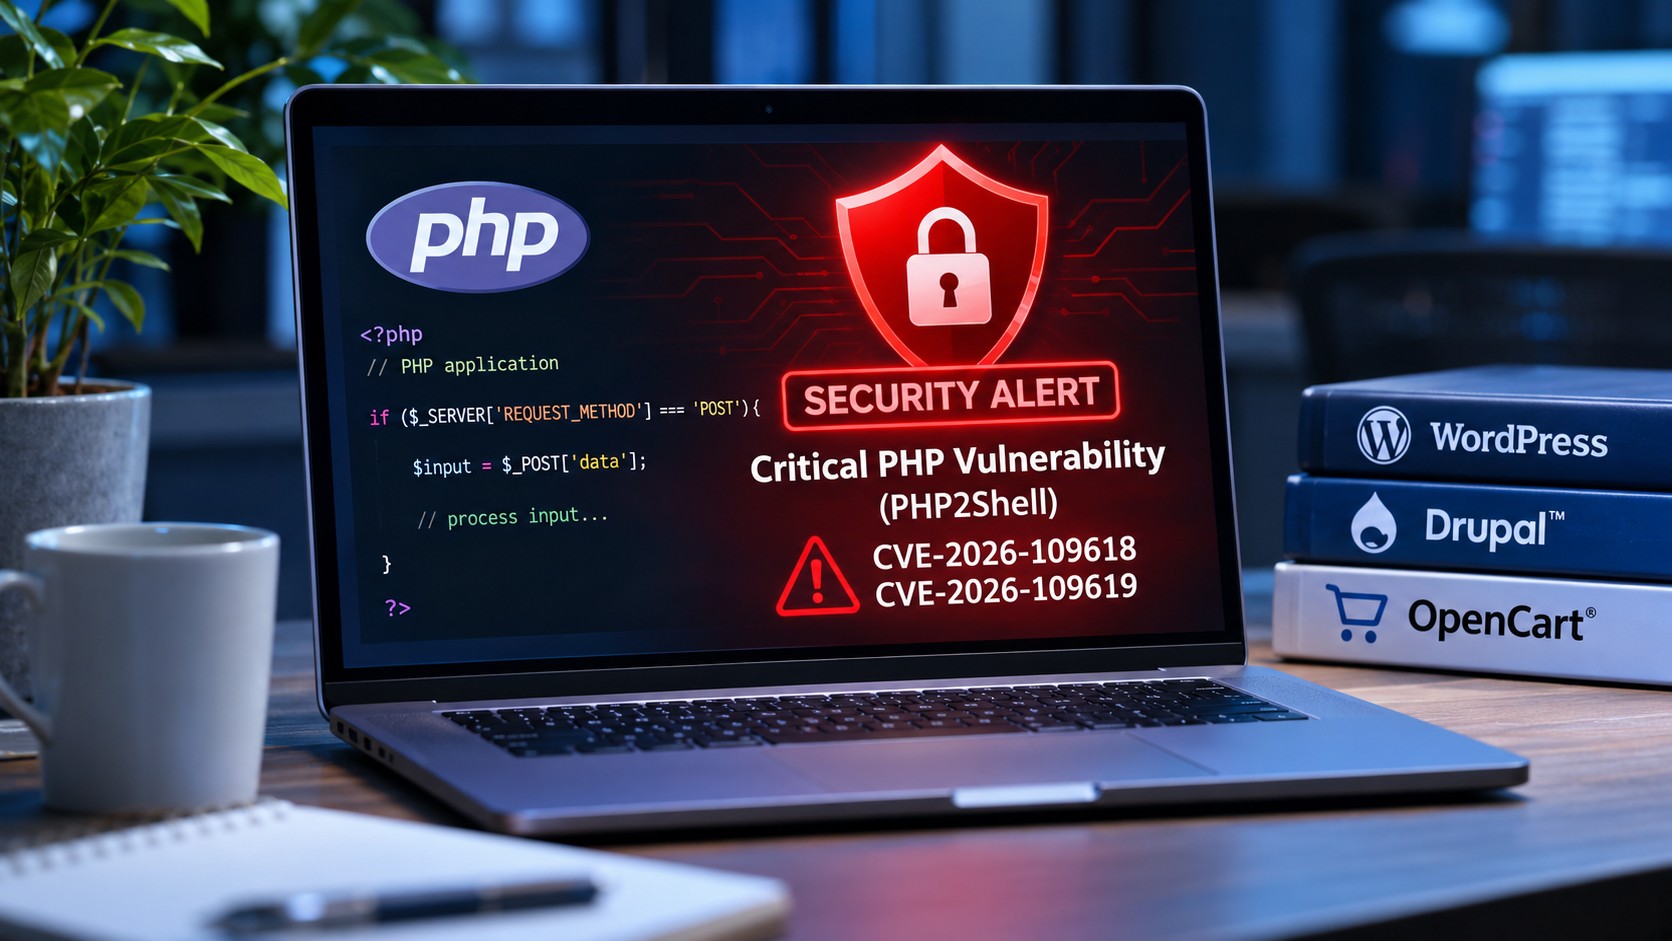
In October 2026, two critical security vulnerabilities were discovered in PHP, the programming language powering millions of websites worldwide. Known collectively as PHP2Shell, these vulnerabilities have raised serious concerns among website owners, hosting providers and cybersecurity professionals.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, received critical severity scores of 9.2 out of 10.
Singapore’s Cyber Security Agency (CSA) has warned of widespread exploitation attempts and urged organisations to apply security updates immediately.
For businesses using WordPress, Drupal, OpenCart or other PHP-based platforms, understanding these vulnerabilities is essential to protecting their websites and customer information.
What Exactly Is the PHP Vulnerability?
PHP is a server-side programming language responsible for processing website functions such as user logins, contact forms, shopping carts, database interactions and content management.
The recently discovered PHP2Shell vulnerabilities involve weaknesses in PHP’s internal memory handling.
Under certain conditions, attackers may exploit these weaknesses to execute malicious code remotely, potentially without requiring a username or password.
This is known as Remote Code Execution (RCE).
If successfully exploited, attackers could potentially:
- Gain unauthorised access to website servers.
- Steal customer information and sensitive business data.
- Inject malicious scripts or redirect visitors to fraudulent websites.
- Modify website files or install hidden backdoors.
- Disrupt website operations or compromise connected systems.
Unlike vulnerabilities affecting individual plugins or themes, PHP2Shell concerns the underlying PHP software itself. Consequently, even a fully updated website application may remain exposed if its server uses a vulnerable PHP version.
How Can PHP Vulnerabilities Affect WordPress Websites?
WordPress depends heavily on PHP to manage website functionality, database interactions, user authentication and content management.
When the underlying PHP environment is vulnerable, WordPress websites may face additional security risks.
1. WordPress Malware Infections
Attackers who successfully compromise a vulnerable server may inject malicious files or scripts into WordPress installations.
These infections can result in spam pages, unwanted advertisements, malicious redirects or unauthorised website changes.
Professional WordPress malware removal and website fixing services can help identify compromised files, remove malicious code and restore website functionality.
2. WordPress Website Errors and Downtime
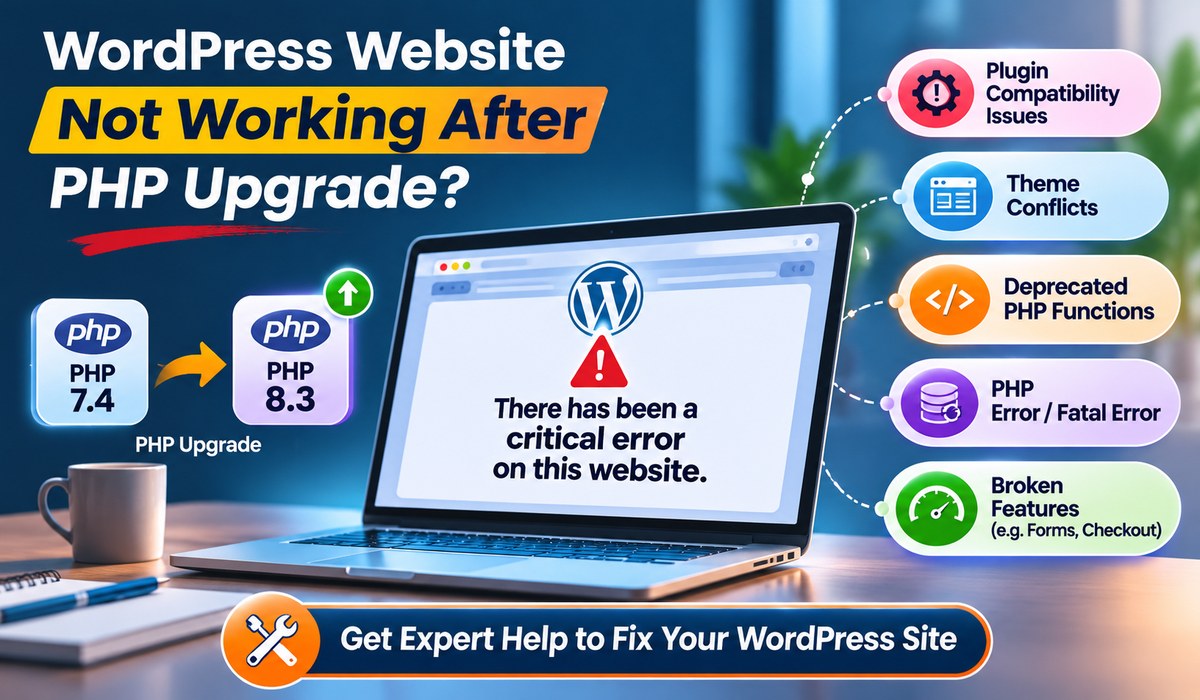
Security incidents and poorly managed PHP upgrades may cause WordPress websites to display critical errors, blank pages or broken functionality.
Common symptoms include:
- WordPress critical error messages.
- HTTP 500 internal server errors.
- White screen of death.
- Broken contact forms or checkout pages.
- Plugin and theme compatibility problems.
An experienced WordPress website repair specialist can diagnose these problems and implement appropriate solutions.
3. Website Performance and Security Problems
Outdated PHP installations may expose websites to known security weaknesses and prevent them from benefiting from newer performance improvements.
Regular WordPress maintenance helps ensure that PHP versions, plugins, themes and server configurations remain compatible and secure.
What About Drupal and OpenCart Websites?
Drupal and OpenCart also depend on PHP, meaning their websites may face similar server-level security risks.
Drupal Websites: Business portals, corporate websites and membership platforms built with Drupal could become vulnerable if their underlying PHP environment remains unpatched.
OpenCart Websites: E-commerce businesses using OpenCart could face risks involving customer records, shopping functionality, order information and website availability.
The actual exposure depends on the PHP version, server configuration, applied patches and other security controls.
Businesses should not assume their websites are protected simply because their content management system is updated.
#3 Scan Your Website for Malware
Conduct a comprehensive security scan to identify suspicious files, unknown administrator accounts, malicious redirects and unauthorised modifications.
#4 Review Website Security
Enable appropriate firewall protection, strengthen administrator passwords, activate two-factor authentication and restrict unnecessary server access.
#5 Establish Regular Maintenance
Website security requires continuous attention. Regular updates, backups, vulnerability monitoring and server checks help minimise future risks.
How Can Professional Web Developers Help?
Many website owners lack the technical expertise to safely upgrade PHP or investigate server vulnerabilities.
An experienced web developer or WordPress maintenance specialist can help by:
- Auditing the website’s PHP version and hosting configuration.
- Applying security patches and resolving compatibility issues.
- Testing WordPress themes, plugins and custom integrations.
- Detecting and removing malware or suspicious code.
- Reviewing server logs for potential security breaches.
- Implementing stronger website and server protection.
- Establishing ongoing backup and maintenance procedures.
Professional assistance is particularly valuable for business-critical websites where unexpected downtime, broken functionality or compromised customer information could result in significant financial losses.
Final Thoughts: Don't Wait Until Your Website Is Compromised
The PHP2Shell vulnerabilities are an important reminder that website security goes beyond installing WordPress updates or security plugins.
The underlying hosting environment, PHP version and server configuration are equally important.
Whether your business website runs on WordPress, Drupal or OpenCart, now is the time to review its security and confirm that the necessary patches have been applied.
Concerned About Your Website’s PHP Security?
If you’re unsure whether your website is running a vulnerable PHP version, contact an experienced web developer for a professional security assessment.
For businesses relying on their websites to generate enquiries, process orders or communicate with customers, these vulnerabilities highlight the importance of professional website technical support, regular website maintenance and timely website fixing services.